If you had all your DATA Stolen Today What would it Cost YOU?
24/7AI POWERED CYBER RESPONSE
ALWAYS WATCHING. ALWAYS EVOLVING.
Threats evolve. So should your defense.
Always watching. Always learning. Always testing. We’re building ARC Hawk to connect round-the-clock AI sentinels, emerging threat intelligence, and continuous attack simulation in one adaptive defense system.
Platform design priorities, not measured performance or customer adoption statistics.
THE ARC HAWK VISION
A connected view. A coordinated response.
From the outer perimeter to the next security decision. Explore how our planned defense layers and agent workflows fit together.
DEFENSE ARCHITECTUREDESIGN CONCEPT
SystemsNetworksAI workloads
123ABC
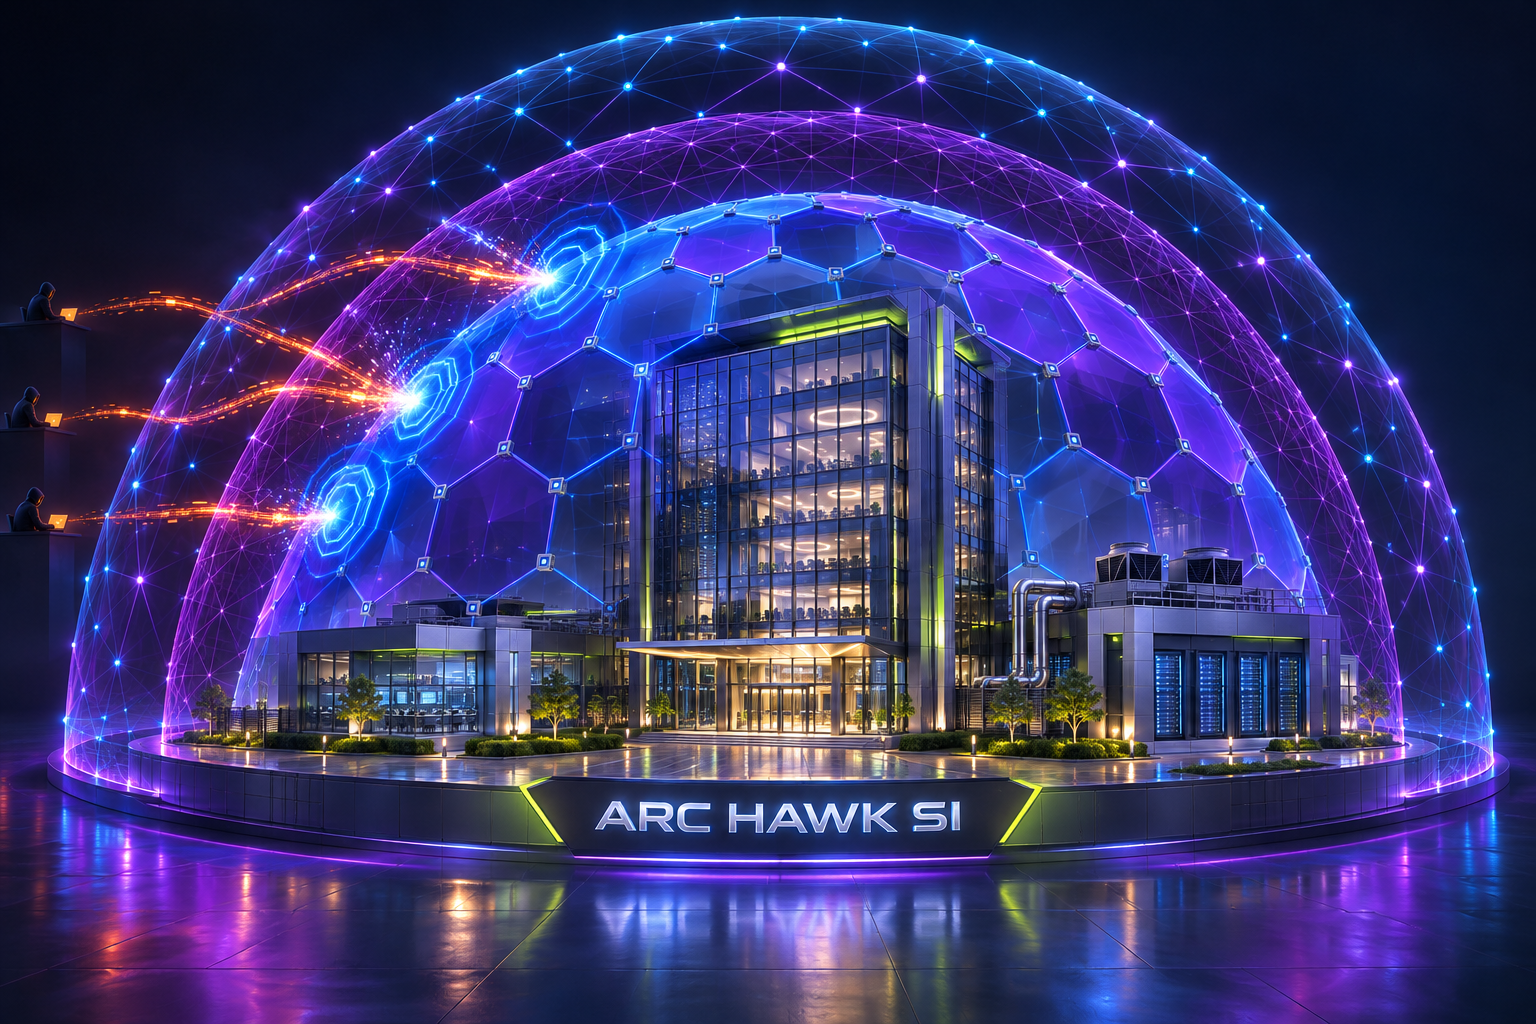
Three layers of adaptive defense
1
Threat intelligence perimeter
Research emerging threats, attacker tactics and new AI-driven techniques.
2
AI attack monitoring
Identify hostile activity and analyze attack patterns approaching the protected environment.
3
ARC Hawk active defense
Octagonal shield: detect, block, isolate and adapt with authorized countermeasures.
What the buildings represent
A
Business systems + data
Endpoints, business applications, sensitive records and operational data.
B
Networks + infrastructure
Corporate networks, identities, servers and connected infrastructure.
C
AI workloads + models
AI agents, model access, prompts, training data and inference services.
Planned coverage depends on validated integrations and the agreed deployment scope.
ARC HAWK / COMMAND VIEWILLUSTRATIVE UI
Defense intelligence
DEFENDObserveSentinel signals
DISCOVERResearchEmerging techniques
VALIDATETestAuthorized scope
ILLUSTRATIVE SIGNAL ACTIVITY · NO LIVE DATA
New technique → controlled testReview evidence. Validate improvements.
→
Interface concept. Not an operating security console.
ONE CONNECTED MISSIONDefend continuously.Test relentlessly.Adapt intelligently.
01 / THE PLATFORM
Three forces. One evolving defense.
Security shouldn’t stand still. Our architecture brings defense, research, and controlled testing into a shared learning cycle.
01 / DEFEND
Sentinels that stay watchful.
AI agents designed to monitor activity around the clock, surface suspicious behavior, and coordinate responses within approved boundaries.
Continuous security monitoring
Context-aware investigation
Policy-controlled response
02 / DISCOVER
Intelligence beyond the perimeter.
Research agents designed to monitor public threat reports, vulnerability disclosures, and emerging attacker techniques—including how adversaries use AI.
Emerging threat research
AI-assisted attack trend analysis
Relevant intelligence for testing
ATTACK SIMULATION
CHALLENGE → VALIDATE → IMPROVE
03 / CHALLENGE
Put our defenses to the test.
Our own AI and SI research systems are being developed to challenge authorized environments, expose weaknesses, and help validate stronger defenses.
Controlled adversarial simulations
Vulnerability validation
Remediation and repeat testing
SECURITY STARTS WITH YOUR PRIORITIES
Real threats. Your environment.
Choose a threat, industry or priority to start your assessment conversation. Coverage and testing methods are confirmed during scoping.
Development priorities and assessment topics. Industry listings do not imply existing customers, certifications or available integrations.
02 / THE CONTINUOUS DEFENSE LOOP
Every lesson. A stronger next move.
A new technique becomes a test. A test reveals a gap. A verified improvement returns to defense. Explore the intended workflow below.
ARC HAWKADAPTIVE DEFENSEContinuous feedback
INTERACTIVE CONCEPT · NOT LIVE TELEMETRY
01 / OBSERVE
Keep watch. Connect the signals.
Sentinel agents monitor authorized systems and gather the context needed to distinguish routine activity from behavior that warrants investigation.
ILLUSTRATIVE WORKFLOW•••
Collect security signals
Correlate activity and context
Escalate according to policy
03 / THE ARC HAWK APPROACH
Think like an attacker. Act like a defender.
We’re designing a system that challenges its assumptions as aggressively as it protects your operations.
[ ARC / RESEARCH AND DEVELOPMENT ]
The next attack should inform the next defense.
As attackers adapt with AI, ARC Hawk’s research direction is to turn emerging techniques into controlled tests—and tested lessons into better protection.
01
Always learning. Carefully updating.
Continuous intelligence informs proposed changes. Validation, approval policies, and rollback plans guide what reaches production.
02
Challenge the systems we’re authorized to test.
Attack simulations stay within owned or explicitly authorized environments. Internet research focuses on threat intelligence—not attacking third parties.
03
Keep people in command.
Our design calls for clear permissions, explainable findings, and human oversight for consequential actions.
YOUR QUESTIONS. CLEAR ANSWERS.
Know what’s behind the intelligence.
A strong security decision starts with evidence. Here’s our current development direction—and what still needs to be validated.
PLANNED ARCHITECTURE Transparent from the start.
How will ARC Hawk learn and stay current?+
Our development plan combines public threat intelligence, authorized test results, and feedback from defensive workflows. These inputs inform proposed detection and response improvements. Model providers, training datasets, retraining schedules, and production update cadence are not yet finalized. Continuous research does not mean unreviewed model changes.
When does a person need to step in?+
The planned design separates routine monitoring from consequential actions. Escalation and approval policies will determine when people intervene. We do not yet have a validated percentage of alerts handled autonomously or a confirmed 24/7 human staffing commitment.
What results can you demonstrate?+
Published customer benchmarks and before-and-after deployment results are not yet available. Evaluation should measure detection quality, false alerts, time to investigate, containment time, and successful retesting against a documented baseline.
How will you control false alarms and model drift?+
Our proposed approach uses contextual correlation, reviewed findings, repeatable test scenarios, and monitoring for changes in detection quality. Threshold changes and model updates should be validated before release, with rollback available. These controls remain subject to implementation and testing.
Can your AI explain a finding or action?+
The design goal is an evidence trail showing the signals considered, the suspected behavior, uncertainty, the recommended action, and the policy governing it. Consequential actions should remain reviewable. This is a development requirement, not a claim of a completed audit feature.
Which environments and tools will you support?+
The initial vision covers authorized systems, networks, and AI infrastructure. Specific operating systems, email and identity coverage, APIs, SIEM connectors, and cloud integrations must be validated before being offered. We will define the supported scope for each deployment rather than assume universal coverage.
Who owns investigation and incident response?+
The planned agent workflows connect monitoring, investigation, testing, and escalation. Service ownership, after-hours human support, containment authority, and response-time commitments have not been finalized. Those responsibilities must be explicit in any future service agreement.
How will pricing and deployment work?+
Pricing, packaging, onboarding timelines, and support inclusions are still being developed. A future proposal should state covered assets, integrations, testing scope, implementation costs, included support, and any additional charges.
What about data privacy and compliance?+
Data location, retention, access controls, permitted model use, and contractual requirements need to be documented before onboarding. This page makes no claim of SOC 2 certification, FedRAMP authorization, or validated regulatory compliance.
Will your agents attack other organizations?+
No. The planned research agents gather threat intelligence from permitted sources. Adversarial simulations target only our own systems or environments where testing has been explicitly authorized, within an agreed scope.
What does AI and SI mean here?+
AI refers to the agent-based intelligence in our planned workflows. SI is ARC Hawk’s designation for its advanced intelligence research direction, not a claim of independently verified superintelligence.
Can we use ARC Hawk now?+
ARC Hawk is in development. This website presents the intended architecture and interface concepts. Production availability and supported capabilities will be confirmed after validation.
ARC HAWK / RESEARCH RADAR
Understand the threat. Advance the defense.
Emerging AI security topics shaping our development priorities. Explore selected industry research and the questions behind our planned defense system.
01 / PROMPT SECURITY
Protect the instructions. Protect the outcome.
Explore how untrusted content can redirect AI agents, and why input boundaries belong in a defense strategy.